I analyse network flows and digital artefacts and document verifiable findings. My Data Engineering experience adds a demand for reliable, traceable data.
Available now · Permanent or fixed-term roles · Angers, open to relocation across France
Open to opportunities in cybersecurity consulting, GRC and CSIRT, as well as PhD projects in academia or industry.
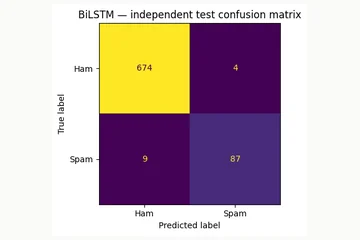
1.29%FGSM attack successdown from 2.07% before hardening · D04
16.43/20MSc averageRanked 1st in semesters 2 to 4
Investigations
Each project handled as a case file: the question, the evidence examined, the finding. Academic projects carried out in authorised labs, alone or in teams, plus one production assignment.
03Differentiator: reliable data pipelines, proven in production.Production experience · D06
04Governance and risk-analysis foundations covered during the MSc.Coursework foundations · EBIOS RM, ISO/IEC 27001
Skills × case files matrix
● skill used in the case file.
Skill
D01
D02
D03
D04
D05
D06
Disk and memory forensics
●
Network analysis
●
●
●
Detection and threshold tuning
●
●
Understanding lateral movement
●
AI model security
●
Data reliability and traceability
●
●
Method
A workflow suited to each project: collect relevant material, examine it, test hypotheses and report the results. For digital forensics, the approach draws in particular on NIST SP 800-86.
01
Collect
Acquire data without altering it and keep a record.
02
Examine
Extract what matters: processes, logs, flows, artefacts.
03
Analyse
Correlate sources and test hypotheses, thresholds included.
04
Report
Write a clear, dated finding that a third party can verify.
Security analysis is only as reliable as the data behind it: trustworthy inputs, effective checks and traceability. At HortiTrace, I applied these principles to production PostgreSQL pipelines; in my cybersecurity projects, they guide how I examine evidence and interpret results.
Skills, tools and frameworks
Built through documented case studies and MSc coursework, with the learning context made explicit for each area.
Detection & SOC Project · coursework
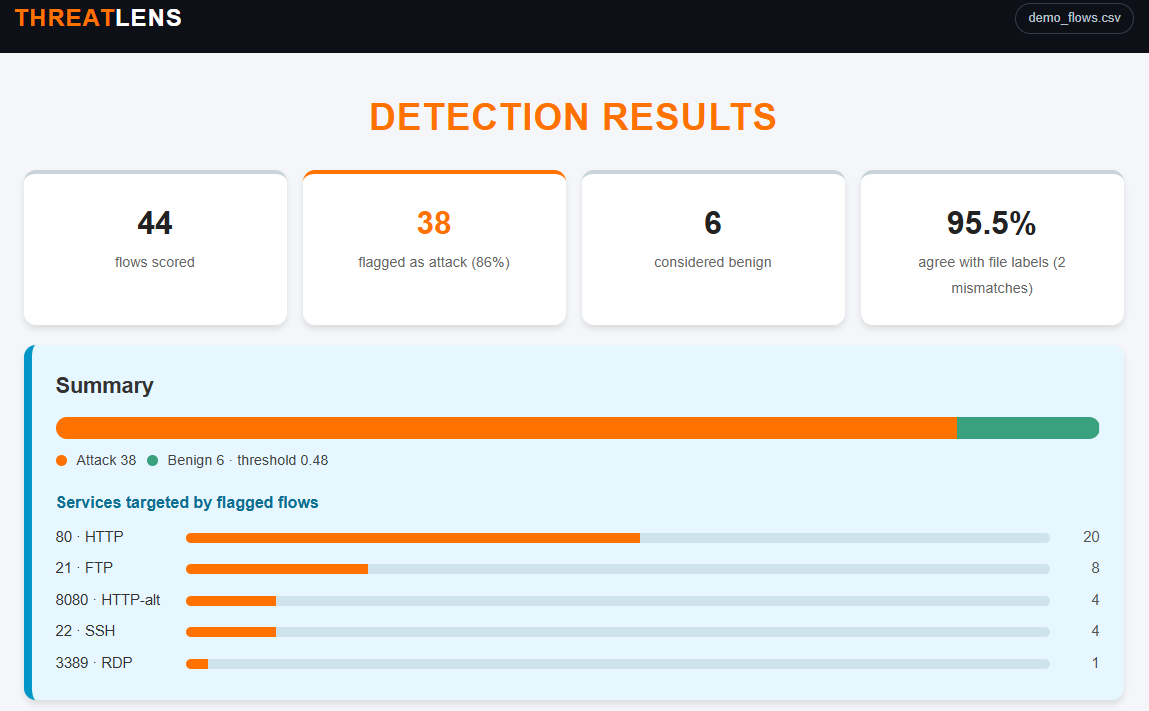
Network-flow analysis, intrusion detection and false-positive evaluation (ThreatLens); log collection and analysis, SIEM/SOC fundamentals, Wazuh/OSSIM studied in coursework.
Investigation & DFIR Cases · labs
Disk, memory and network artefacts; PCAP analysis and timeline reconstruction; Autopsy, FTK Imager, Volatility, Wireshark, HxD.
Networks & offensive security Labs · coursework
TCP/IP, routing, switching, segmentation, SSH; Nmap, Ligolo-ng, Linux (Kali, Ubuntu, Debian); academic pentesting methodology and the “Certified Ethical Hacker” (CEH) course taken at ESAIP.
GRC & incident management Coursework
Risk management and cyber crisis management, IT governance, data protection and Privacy by Design; incident-response principles.
Systems, cloud & cryptography Labs · coursework
Windows/Linux, Active Directory fundamentals (identities, accounts and access permissions), Microsoft Azure fundamentals (AZ-900 coursework), cryptography concepts and data security; Docker.
Security Analytics & scripting Projects · Data production
NIST SP 800-86 for digital forensics; MITRE ATT&CK (foundational knowledge); EBIOS RM, ISO/IEC 27001 and GDPR.
Background
Experience
11/2025 – 05/2026
Data Engineer, final-year internship · HortiTrace SAS, France
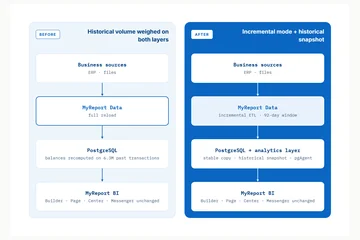
Optimised a production PostgreSQL ETL chain: incremental loading and a pre-aggregated reporting layer, then validation through 7 supervised regression tests, with no discrepancy found within the verified scope. Case file D06
06/2025 – 08/2025
BI Developer, academic internship · Alshadows Technologies, Cameroon
Designed a BI prototype on demonstration data: 9-table SQL Server model, Power Query preparation, 20+ DAX measures and 4 Power BI pages.
10/2020 – 08/2022
IT Consultant · HPS International Consulting, Cameroon
Data security checks, backups and patching; business requirements analysis, integration of information systems (ERP, business applications), IT project follow-up and user support.
11/2019 – 10/2020
IT Applications Analyst · Will & Brothers Consulting, Cameroon
Optimised a TensorFlow vehicle-detection API (accuracy raised from 73% to 88%) and integrated inventory-monitoring dashboards.
Education
02/2024 – 10/2026
MSc Cybersecurity & Data Science (Bac+5 level) · ESAIP Engineering School
Average 16.43/20, ranked 1st in semesters 2 to 4. Detailed results
06/2022 – 12/2023
MSc Technical Education (CSE), first year completed · IUT, Bangladesh